

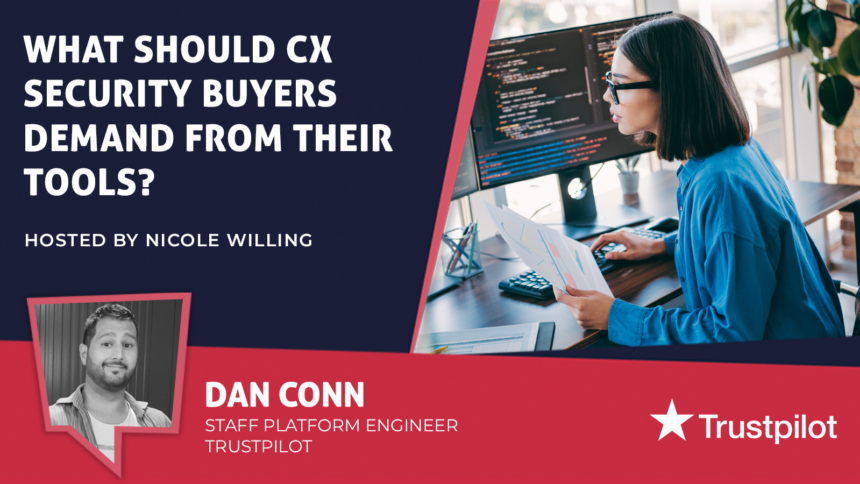
As vulnerability volumes grow, CX technology leaders need security tools that do more than generate alerts. Trustpilot’s Dan Conn explains why prioritizing customer-facing risk can reduce remediation work and prevent avoidable vulnerabilities reaching production, protecting customer trust.
Cybersecurity teams are under mounting pressure to remediate vulnerabilities quickly, while engineering teams must keep delivering the reliable digital services customers expect. That makes security tooling a customer experience decision as much as a technical one.
The challenge for CX tech buyers is choosing technologies that reduce the number of issues engineers need to manage, without slowing product delivery or creating new operational burdens.
The rising volume of vulnerabilities makes this increasingly urgent, Dan Conn, Staff Platform Engineer at Trustpilot, told CX Today.
“We’re finding that just as many vulnerabilities in recent years are found than the 10 previous years or five previous years. That’s quite a remarkable uptick. It’s something that we’re all going to struggle with going forward.”
While AI can help security researchers find vulnerabilities, it may also speed up the discovery of flaws that attackers can exploit. Conn pointed to a recent example in which AI, working alongside a researcher, identified an exploit affecting multiple software versions.
A security approach built around ever-growing queues of alerts will not scale. Instead, the first buying priority should be better prioritization, acknowledging that a high Common Vulnerability Scoring System (CVSS) score does not automatically mean a flaw poses the highest risk to customers or the business.
“In particular, just relying on CVSS scoring, that can be quite problematic,” Conn said. “A lot of the base scores don’t take into account the temporal environment scores that you meant to add anyway.”
At Trustpilot, teams use a combination of signals, including CVSS severity, Exploit Prediction Scoring System (EPSS) exploitability data and whether a vulnerability can genuinely affect their own environment, Conn said. They also consider customer exposure.
“The main overriding factors are, is it on the perimeter? Is it something that a customer can touch? That would be the first thing to get sorted.”
For CX tech buyers, that means asking potential vendors whether they can help teams rank risks by real-world exploitability, internet exposure, affected services and customer impact. While tools that simply generate an inventory of vulnerabilities can create more triage work, more useful platforms help teams identify the issues that could interrupt a customer journey, expose customer data or affect service trust.
Trustpilot is a customer of software supply chain security company Chainguard, using its hardened container images as part of this effort. The relationship illustrates the shift in security buying from tools that report a problem to products that remove a common source of risk before it reaches developers and production systems.
Conn describes Trustpilot’s approach as “start left,” building on the established principle of shifting security earlier in the software-development lifecycle. But the aim is not simply to give developers more security tasks.
“More from a security side standpoint of ‘start left,’ this is like ‘secure by default,’” Conn said.
Containers are essential to cloud-native organizations, but maintaining hardened images internally can be time-consuming and error-prone. Teams must continually remove vulnerabilities, manage dependencies and maintain their own secure foundations.
“Where Chainguard comes in really well with this is, it takes away a massive problem for us, which is vulnerabilities within containers,” Conn said.
Conn previously worked in an organization that created its own hardened images. “It’s a very laborious process. It’s very error-prone. You have to remove all the vulnerabilities in your system and manage that whole thing.”
For Trustpilot, using Chainguard’s hardened images means engineers start with a more secure base rather than inheriting container vulnerabilities they did not introduce directly. “They’re not worrying about updating their vulnerabilities in the container,” Conn said.
This is significant for customer experience leaders because much of the security work that affects customer-facing services stems from transitive dependencies such as components included through other software packages rather than selected deliberately by a developer. These issues still need attention, but reducing them at the foundation frees engineering teams to focus on the code and services that differentiate the customer experience.
The practical question for buyers is whether a security tool reduces remediation work, prevents known risks from entering the delivery pipeline or helps teams maintain secure defaults at scale. Conn said:
“We’re certainly looking at tooling that solves a problem. There’s a lot of them that detect a problem and that’s great as well. Visualization’s great, but if it’s not actually doing something for you, then it can be a bit difficult.”
That distinction is particularly important when securing executive support. “It’s great that it tells me something,” Conn adds, “but what is it actually fixing for me?”
Buyers should also avoid applying a one-size-fits-all approach. The right investment depends on an organization’s data, services and risk profile.
“What’s very important is to understand your own posture,” Conn said.
The immediate action for CX technology leaders is to map customer-facing systems, the data they handle and the dependencies they rely on. Then assess tools based on whether they reduce the risks in those areas, rather than just adding to the list of issues teams already need to investigate.
As Conn put it, “We try to look at the security of the product as… a value add.” The strongest security investments will make that value visible through safer customer services, less engineering toil and faster, more reliable delivery.
Does this reflect your experience?
Buyers Need Cybersecurity Tools That Fix Problems, Not Just Flag Them – CX Today


Leave a Comment